


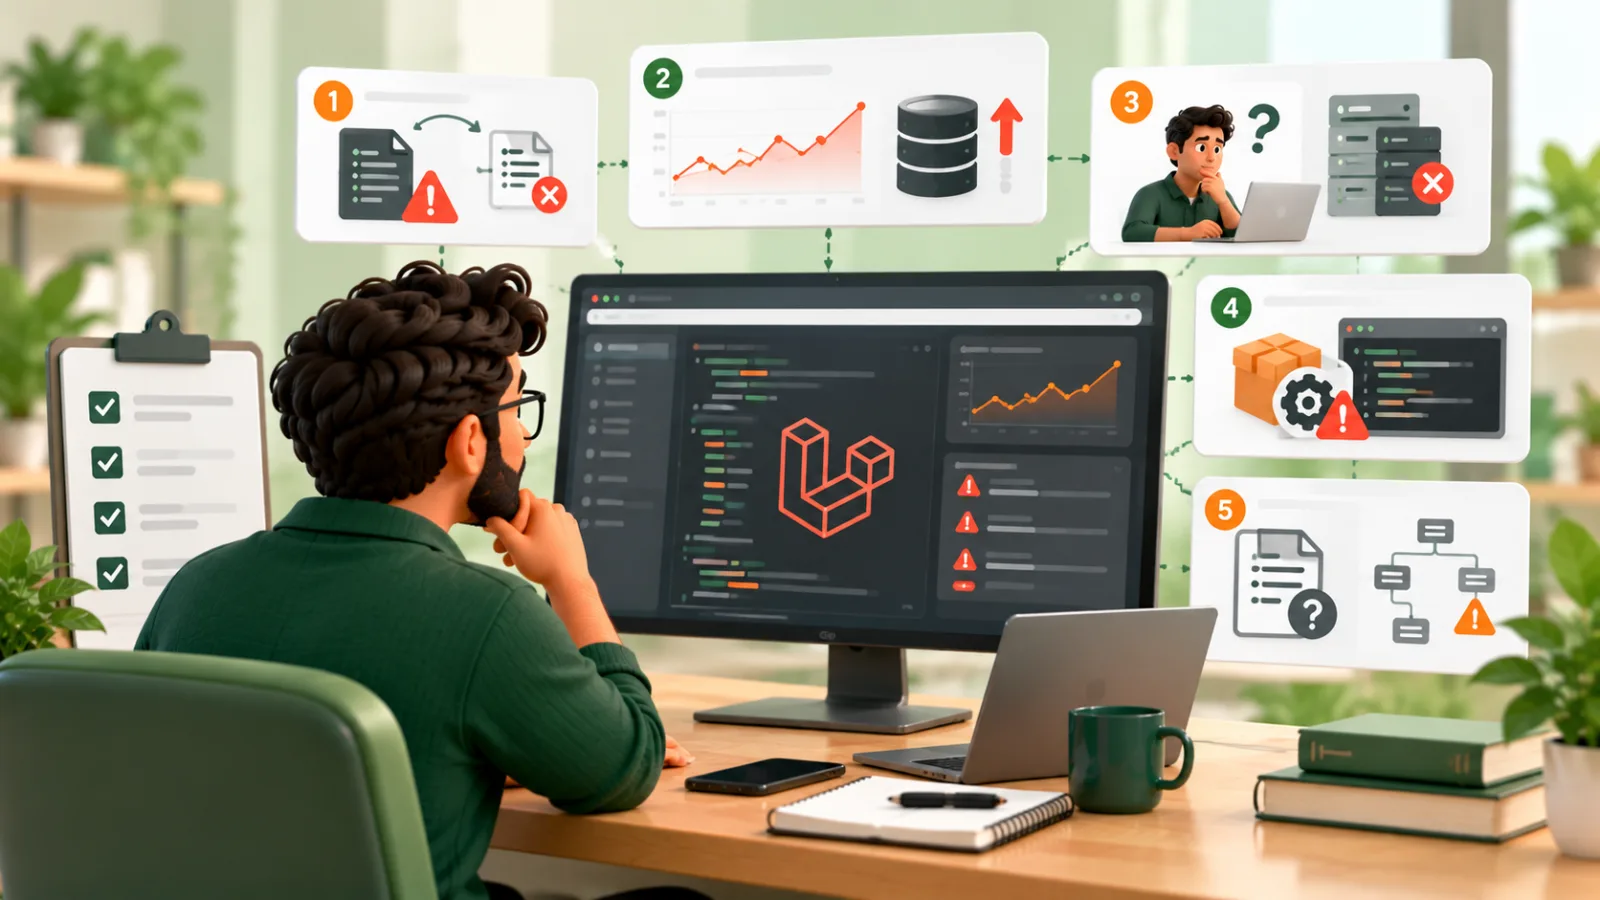
A Laravel application may benefit from a technical review when releases repeatedly break unrelated features, important pages slow down as data grows, onboarding becomes difficult, dependency updates are avoided, or business rules are hard to explain. These are prompts for investigation, not proof that the application needs rebuilding.
A focused review should connect each symptom with evidence and a prioritized next step. This guide explains five signs to look for, what to prepare, and the deliverables to request from a Laravel development team.
1. Small changes cause unrelated failures
If a routine update breaks another customer journey, review how the affected features depend on one another and which tests cover them. Start with a recent incident, the change that preceded it, and the actual behavior users experienced.
Ask the reviewer to identify critical flows that need regression coverage and changes that can reduce unnecessary coupling. Avoid treating every regression as evidence of a weak developer; unclear requirements, missing test data, and deployment differences can contribute too.
The useful outcome is a repeatable way to check a change before release, with someone responsible for resolving failures.
2. Response times worsen as data grows
Collect a representative slow request, its response time, the data volume, and the queries or services involved. Compare development, staging, and production conditions before assuming a local result explains the customer experience.
Possible causes include repeated queries, missing indexes, unnecessarily large result sets, external service delays, or work that could run asynchronously. A review should measure these paths before recommending caching, more servers, or a framework change.
Our Laravel performance optimization guide describes the investigation sequence. Every proposed change should include a way to compare behavior and performance before and after it.
3. New developers cannot reproduce the application reliably
Ask a team member to follow the setup instructions in a clean development environment. Record undocumented steps, unavailable test fixtures, missing service configuration, and dependencies on a colleague's machine.
Then trace one important workflow through its inputs, permissions, validation, data changes, and output. Difficulty finding the behavior may point to documentation or structure that has fallen behind the product.
Request reproducible setup instructions and explanations of the important boundaries. A new directory structure alone does not establish that the application is easier to maintain.
4. Dependencies and deployment steps are difficult to update
Record the actual PHP, Laravel, database, and package versions. Compare them with the support policies and upgrade documentation for those versions. A release can still run while no longer receiving the support your business requires.
Laravel publishes its release and support policy. Use that source rather than assuming an application is supported because it was updated recently. Review third-party packages separately.
Plan updates in staging with backups, checks for important workflows, and a rollback approach. The Laravel deployment documentation should be read for the application's target version; commands and infrastructure choices need to fit the actual release.
5. Important business rules have no clear explanation
Choose a rule involving money, permissions, approvals, or a customer-facing commitment. Ask where it is implemented, which conditions change the result, and how the team verifies it.
When behavior is spread across several layers, the reviewer should describe the current rule before proposing a replacement. An unusual path may reflect an important business exception that would be lost in a broad cleanup.
Write down the examples that matter and convert them into acceptance criteria or appropriate automated tests. Keep the business owner involved in confirming that the explanation is correct.
What to prepare for a Laravel technical review
- A list of the most important customer and staff workflows.
- Recent errors, performance measurements, and deployment incidents.
- The application's version inventory and normal release procedure.
- Access to an appropriate repository and staging environment through an agreed process.
- Known constraints, upcoming deadlines, and the person who accepts recommendations.
Do not place passwords or production secrets into a public brief. Agree access separately and use representative test data where possible.
What should the review deliver?
Request findings with evidence, their effect on the business, suggested priorities, dependencies between fixes, and estimates or further questions for the next stage. Separate urgent issues from maintainability improvements and optional redesigns.
A review should explain where confidence is limited. For example, a missing production trace may prevent a precise performance diagnosis. Naming that gap is more useful than making a confident recommendation without measurements.
Use a software requirements document to record the important behavior and acceptance criteria, and agree what follow-up validation is included.
Does a review mean a rebuild is necessary?
No. Focused improvements may address the main risks without replacing the application. Consider a rebuild only after comparing the requirements, constraints, migration effort, and costs of improving the existing system.
Choose one symptom to investigate first
Describe the Laravel issue to RuhaniSoft with a reproducible example and the effect on users. Start with evidence and an agreed review scope so the next development decision can be evaluated.